- Client
- My own product
- Role
- Design, cryptography, development
- Year
- 2026
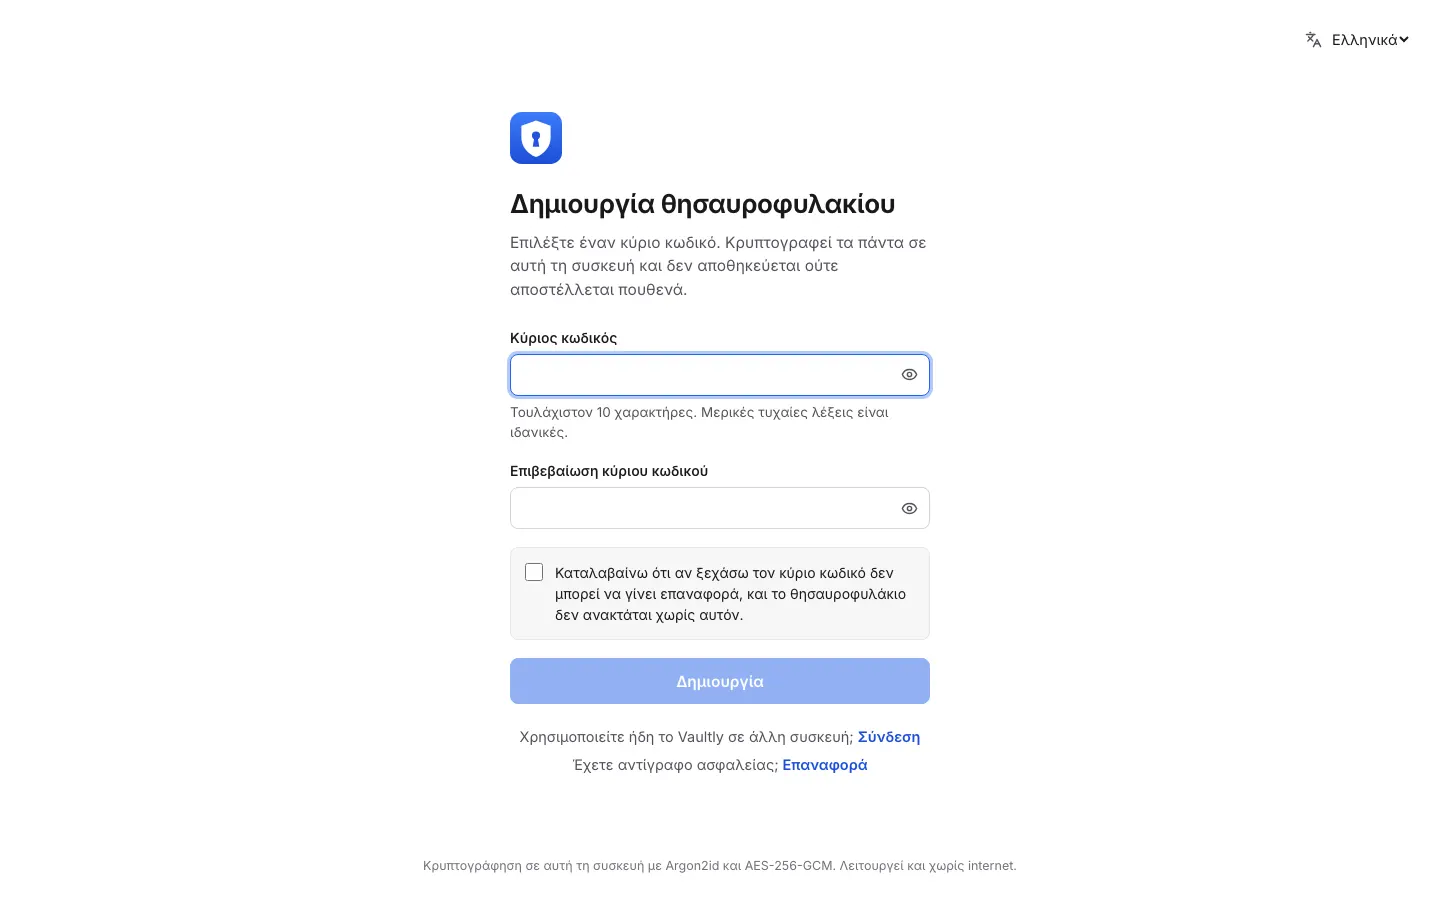
The challenge
Passwords are the most sensitive data we have. I wanted something fast that also works offline, without having to trust any server.
The solution
All encryption happens on your device. The server stores only ciphertext, so even a leak reveals nothing.
How it was built
The technology at every layer, from the screen down to the infrastructure.
- Websites
- Svelte 5
- PWA
- IndexedDB (offline)
- Apps
- Argon2id in WebAssembly
- AES-256-GCM
- HMAC login key
- Hosting & cloud
- Cloudflare Workers
- D1
- Strict CSP
- Networks & ITNot needed
Key technical decisions
Zero-knowledge
The master password never leaves the device. The server keeps only ciphertext and a login key that reveals nothing.
Strong encryption in the browser
Argon2id with 64 MiB of memory in WebAssembly, making brute-force attacks impractical.
Hardened sessions
__Host- cookies, CSRF protection, rate limits and no hint of whether an account exists.
What it includes
- Argon2id & AES‑256 encryption
- Works offline as an app
- Encrypted sync
- Import from 1Password, Bitwarden and more
- Breached-password check
The result
Live at vaultly.emmanouilkontos.com, with import from the most popular password managers.